
About Dashboard and Self Service Report Permissions
Dashboard and self service report permissions allow you to permit your entire tenant, groups within your tenant, or users within your tenant to read, write, or delete a dashboard or report. This allows you to share a dashboard or report with other users. If a user belongs to a group that has the Administer Dashboards privilege enabled, the user can read, add, modify, or remove any dashboard or report in the tenant. However, if the user does not belong to a group with this privilege enabled, the user can still be granted permission to read, write, or delete specific dashboards and reports in the tenant using dashboard permissions. Dashboard permissions allow users in an tenant or group to read, write, or delete a dashboard or report, regardless of any group privilege settings that ordinarily limit their ability to do so.To manage permissions of a dashboard or self service report, a user must meet one of the following criteria:
- Must be an administrator, belonging to the Administrators group or Content Distributors group.
- Must belong to a group with the Administer Dashboards (ROLE_ADMINISTER_DASHBOARDS) privilege enabled.
-
Must belong to a group with the Manage Dashboard Permissions (ROLE_PERMISSION_DASHBOARDS) privilege enabled. If your user definition has only this privilege (and not the Administer Dashboards privilege), you will only be able to manage permissions for the dashboards or reports for which you have
READpermission. In addition, you may be restricted in which permissions you can assign. You can only assign permissions equivalent to your own. For example, if your user account has read permission for a dashboard or self service report, you can grant and revoke the read option available on the Permissions panel. If you have write permission for a dashboard or self service report, you can grant and revoke the write option on the Permissions panel.If your user account does not have read permission for a dashboard or self service report, you cannot see the dashboard or report in the appropriate Library.
GET /api/dashboards/{dashboardId}/acls, PUT and PATCH /api/dashboards/{dashboardId}/acls/bulk, GET /api/inventory/DASHBOARD/{id}, and GET /api/user/permissions/dashboards/{dashboardId}.
API documentation is provided in your environment at this link: https://<Self-Service Analytics-URL>/composer/swagger-ui.html.
- Users who have the group privilege Export Dashboards (ROLE_EXPORT_DASHBOARDS) and READ for dashboards can export dashboards.
- Users who have group privileges of Manage Connections (ROLE_MANAGE_CONNECTIONS), and Administer Sources (ROLE_ADMINISTER_SOURCES), and Administer Visuals (ROLE_ADMINISTER_VISUALS), and Administer Dashboards (ROLE_ADMINISTER_DASHBOARDS) can import dashboards.
Grant Permissions for a Dashboard
You can grant read, write, or delete dashboard permissions for your tenant, groups in your tenant, or specific users in your tenant.In this release, when your admin enables the Enhanced Experience user interface, you will see changes to workflows you may have used in previous releases.
- Log in as an administrator or a user belonging to a group that includes the Administer Dashboards or the Manage Dashboard Permissions privilege. If you are logged in as a tenant admin, verify you’re in or switch to the appropriate tenant.
- Select the Discovery Board card on your home page or Library from the main menu. The dashboard library opens.
-
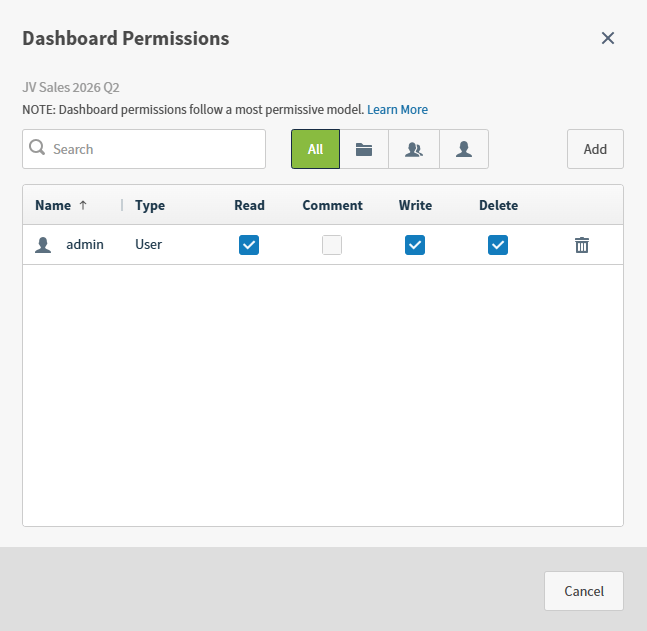
Locate the row for the dashboard in the list and select the permissions icon in the Permissions column. The Dashboard Permissions dialog appears.
-
Select Add on the Dashboard Permissions dialog and then select Groups, Users, or Tenant from the drop-down menu.
- If you select Groups, the Add Groups dialog appears, listing all the groups available in your tenant. The supplied groups are not shown; permissions can not be changed for those groups.
- If you select Users, the Add Users dialog appears, listing all the users available in your tenant.
- If you select Tenant, Read permission is selected for your tenant on the Source Permissions dialog.
- Members of the Administrators group have data access, read, write, and delete permissions for every data source in the tenant.
- The user who creates a data source is automatically selected and has Data Access, Read, Write, and Delete permissions unless you revoke these permissions.
-
Select tenants or any specific groups or users you want to permit to read, write, or delete the dashboard and select Apply. The Dashboard Permissions dialog lists your selections.
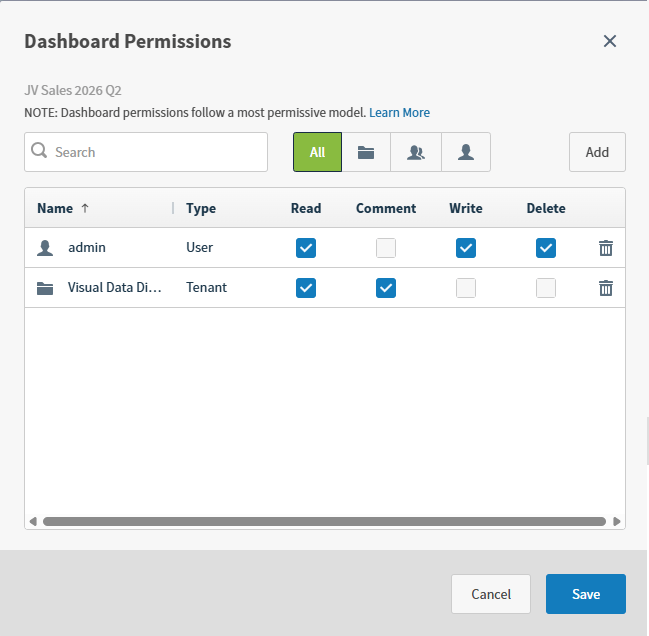
- Select the Read, Comment, Write, or Delete checkboxes for a tenant, groups, or users to indicate what they can do with the dashboard. Read permission is assumed and is always selected. If you clear (uncheck) the Read box (revoke Read permission), permission for the entire dashboard is revoked for the tenant, group, or user after you save.
-
Select Save. The Save Details dialog appears, listing the changes that you made.
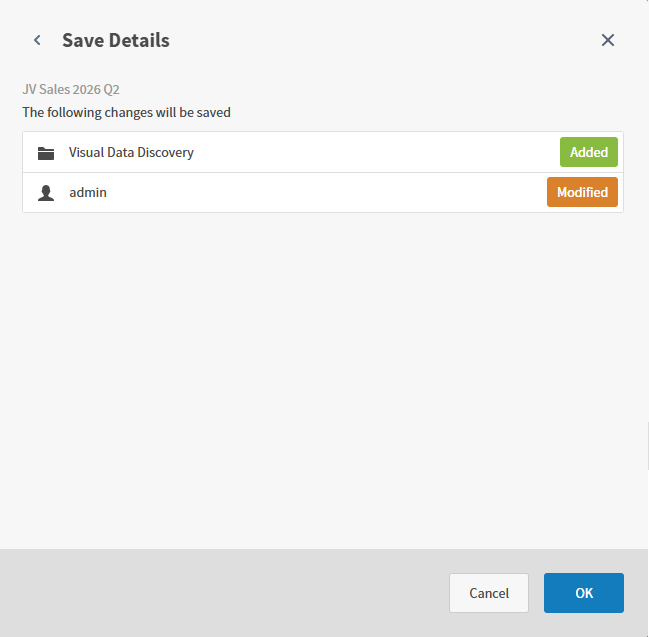
- Review the changes and select OK. The dashboard permissions are set.
Modify Permissions for a Dashboard
You can modify the dashboard permissions you granted to your tenant, to groups in your tenant, or to specific users in your tenant.In this release, when your admin enables the Enhanced Experience user interface, you will see changes to workflows you may have used in previous releases.
- Log into Self-Service Analytics as an administrator or a user belonging to a group that includes the Administer Dashboards or the Manage Dashboard Permissions privilege.
-
Select the Discovery Board card on your home page or Library from the main menu. The dashboard library opens.
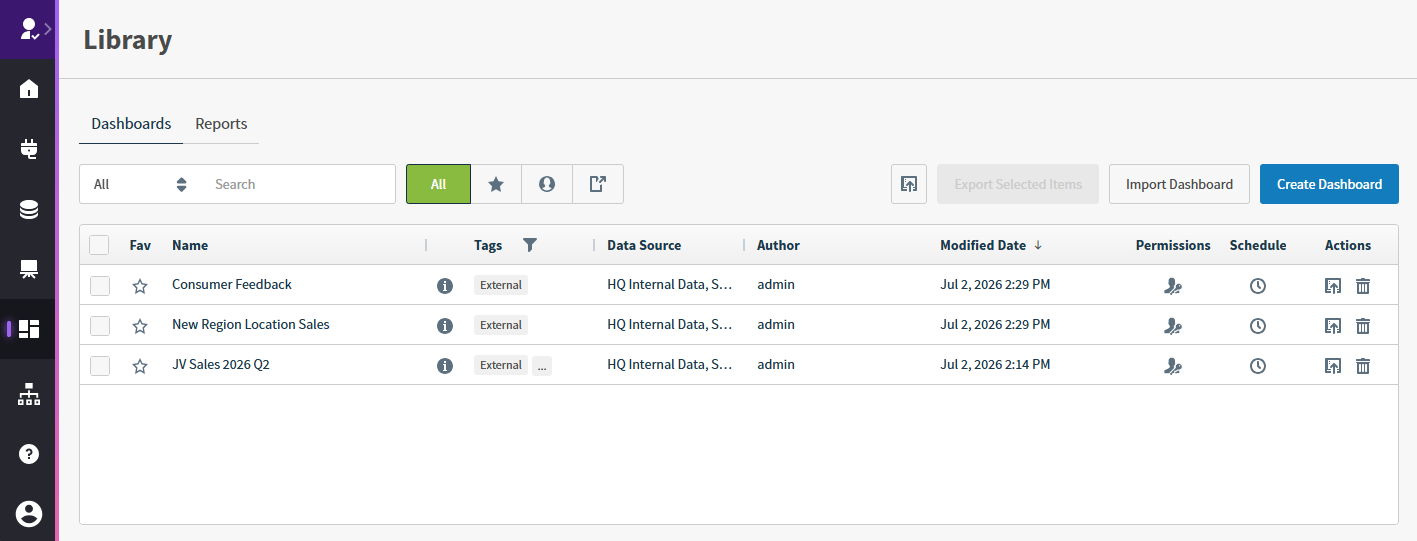
- Locate the row for the dashboard in the list and select the permissions icon in the Permissions column. The Dashboard Permissions dialog appears, showing current rights for tenants, groups, and users. Some columns in this work area can be resized or sorted as needed; select the column header break to resize, or select the column name to change the sort.
-
If you want to add permissions for all users in your tenant or for additional groups or users in your tenant, select Add on the Dashboard Permissions dialog and then select Groups, Users, or Tenant from the drop-down menu.
- If you select Groups, the Add Groups dialog appears, listing all the groups available in your tenant. The supplied groups are not shown; permissions can not be changed for those groups.
- If you select Users, the Add Users dialog appears, listing all the users available in your tenant.
- If you select Tenant, Read permission is selected for your tenant in the Dashboard Permissions dialog. When finished, select Apply.
- Members of the Administrators group have read, write, and delete permissions for every dashboard in the tenant.
- The user who created the dashboard is automatically selected and has Read, Write, and Delete permissions, although these permissions can be changed.
- Modify the Read, Write, or Delete checkbox selections for the tenant or any of the users or groups on the Dashboard Permissions dialog to indicate what users in them can do with the dashboard. Read permission is assumed and is always selected. If you clear (uncheck) the Read box (revoke Read permission), permission for the entire dashboard is revoked for the tenant, group, or user after you save.
- Select Save. The Save Details dialog appears, listing the changes that you made.
- Review the changes and select OK. The dashboard permissions are set.
Revoke Permissions for a Dashboard
You can revoke the dashboard permissions you previously granted to your tenant, to groups in your tenant, or to specific users in your tenant.In this release, when your admin enables the Enhanced Experience user interface, you will see changes to workflows you may have used in previous releases.
- Log into Self-Service Analytics as an administrator or a user belonging to a group that includes the Administer Dashboards or the Manage Dashboard Permissions privilege.
- Select the Discovery Board card on your home page or Library from the main menu. The dashboard library opens.
- Locate the row for the dashboard in the list and select icon in its Permissions column. The Dashboard Permissions dialog appears. Some columns in this work area can be resized or sorted as needed; select the column header break to resize, or select the column name to change the sort.
- To completely revoke all dashboard permissions for the tenant or for a group or user, locate the row for the tenant, group or user on the Dashboard Permissions dialog and select the delete icon. The tenant, group, or user is removed from the dialog. You can also revoke specific permissions by changing the checkbox selections for the tenant or group on the Dashboard Permissions dialog. If you clear (uncheck) the Read box (revoke Read permission), permission for the entire dashboard is revoked for the tenant, group, or user after you save. See Modify Permissions for a Dashboard.
- Select Save. The Save Details dialog appears, listing the changes that you made.
- Review the changes and select OK. The dashboard permissions are set.